#nodejs
36 posts · Last used 2h
What's new in Node.js 27 by @loige@mastodon.ie https://lobste.rs/s/vtjjbc #javascript #nodejs
https://nodejsdesignpatterns.com/blog/whats-new-in-nodejs-27/
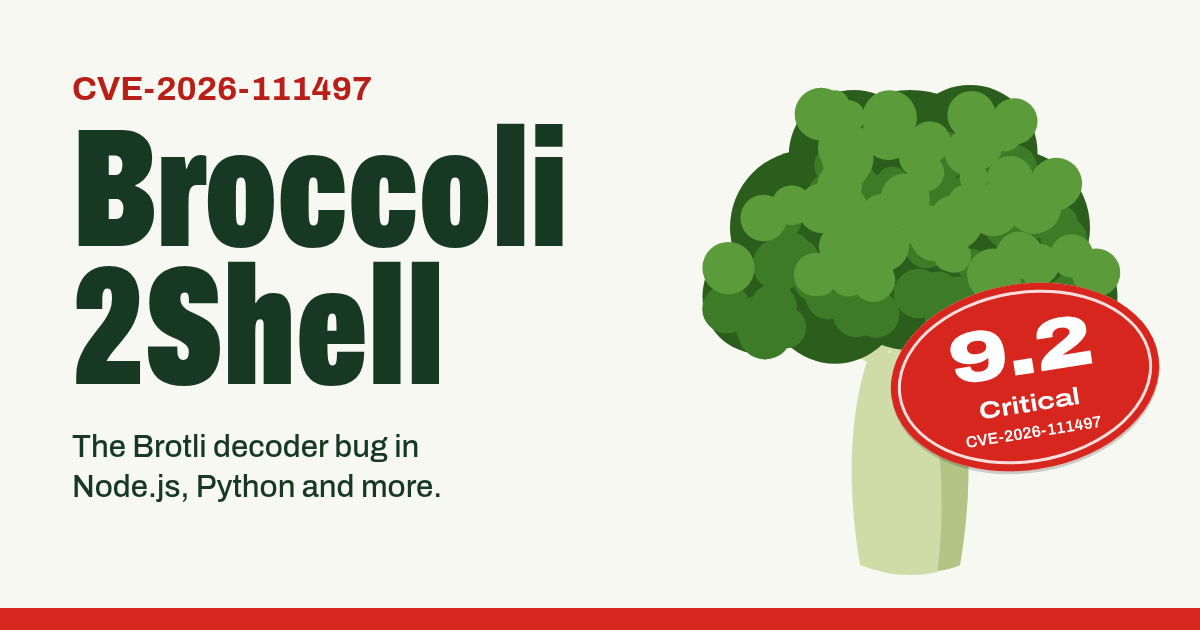
Broccoli2Shell: the Brotli decoder bug (CVE-2026-111497) - Affecting Node.js, Python, C library
CVE-2026-111497 (Broccoli2Shell, aka Node2Shell): an out-of-bounds write in Google’s Brotli decoder affecting Node.js, Python Brotli/brotlicffi and anything built on the C decoder. Affected versions, how to check, and how to fix it.
Boosted by @oxy@social.bsdlab.au
#FreeBSD #Portslife #NodeJS any nodejs users could help me out and test https://bugs.freebsd.org/bugzilla/show_bug.cgi?id=300001 https://nodejs.org/en/blog/vulnerability/october-2026-security-releases that would be great, just to have a few more eyes on it than just myself.
Node.js — Wednesday, October 21, 2026 Security Releases https://lobste.rs/s/gu7bow #javascript #nodejs #security
https://nodejs.org/en/blog/vulnerability/october-2026-security-releases
Removing a Type Assertion with Object.assign https://lobste.rs/s/l5oolm #nodejs #web
https://ataias.com.br/2026/10/01/removing-a-type-assertion-with-object.assign/
Friendship ended with Deno, now Node is my best friend https://lobste.rs/s/a9kwzv #nodejs
https://dbushell.com/2026/10/03/deno-to-node/
Fake Express Packages on npm Spread a Linux Worm https://lobste.rs/s/e2gxro #linux #nodejs #security
https://safedep.io/dirtyblanket-express-impersonation-npm
Fake Spotify, Zoom and Teams installers are being used in ClickFix attacks to spread ChainScript, a Node.js RAT that uses Polygon smart contracts to locate its C2 server.
Listen/Read: https://hackread.com/clickfix-chainscript-rat-fake-spotify-teams-installers/
#Cybersecurity #Malware #ClickFix #ChainScript #NodeJS #Polygon
Ma quanto è semplice fare siti web semplici e veloci con Astro? L'ho scoperto due giorni fa grazie al toot di un utente che però non ritrovo perché ho dimenticato di mettere la stellina.
Comunque si cerca un tema sul sito ufficiale di Atsro, si clona da github, si modifica a piacimento e poi sempre tramite github si può mettere tutto su netlify in pochissimi passi.
Ecco il mio blog:
https://linuzz-zen.netlify.app/
#sviluppoweb #astro #nodejs
LOOKING FOR A JOB
https://nemo.earth/#barto
SKILLS
Frontend mostly, JS mostly, Svelte React Vue Ionic mostly. But often after work day I was developing fullstack apps, with NodeJS as backend. Coding also in raw PHP. And maybe will return to Python. Besides of course GIT, HTTP, Rest, SOLID, Keep It Simple, etc.
COOPERATION
Contract B2B with my one-person company.
SALARY
Fair enough for Mid+ / Senior.
IMPORTANT
I don't use AI while coding. And don't want to!
#job #cooperation #frontend #backend #fullstack #noai #javascript #nodejs #svelte #ionic #php #react #vue
Boosted by @_elena@mastodon.social
Hey folks, can you help me out with a little something: trying to come up with a good number of files limit for a file scan (for Kitten so you don’t hit heap memory limits if you run it from the wrong directory by mistake) and I’d love some statistics from real JavaScript/TypeScript Node.js projects of the number of files in them (excluding .git and node_modules).
Would you be kind enough to run the following command in Terminal in your largest projects and let me know what number your get (along with a short description of the project):
find . \( -name "node_modules" -o -name ".git" \) -prune -o -print | wc -l
Thank you :)
#Kitten #SmallWeb #SmallTech #NodeJS #web #dev #stats #helpWanted
2026-07-29, Version 24.18.1 'Krypton' (LTS), @juanarbol
This is a security release. Notable Changes (CVE-2026-56846) http2: retain header memory in session accounting (Matteo Collina) – High (CVE-2026-56848) http2: defer rst stream while in scope (Matteo Collina) – High (CVE-2026-58043) permission:...
https://github.com/nodejs/node/releases/tag/v24.18.1
#nodejs #javascript
Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
#NodeJS #CVE202656848 #HTTP2 #UseAfterFree #Vulnerability #InfoSec
2026-07-29, Version 22.23.2 'Jod' (LTS), @marco-ippolito
This is a security release. Notable Changes (CVE-2026-56846) http2: retain header memory in session accounting (Matteo Collina) – High (CVE-2026-56848) http2: defer rst stream while in scope (Matteo Collina) – High (CVE-2026-58043) permission:...
https://github.com/nodejs/node/releases/tag/v22.23.2
#nodejs #javascript
v1.19.0
v1.19.0 - July 22, 2026 This release raises the form-data security floor, adds configuration and type-system capabilities, and fixes NO_PROXY matching, interceptor errors, progress reporting, and serialization edge cases. 🔒 Security...
https://github.com/axios/axios/releases/tag/v1.19.0
#axios #nodejs
Replying to
@rees@tsundere.love @p@fsebugoutzone.org @mischievoustomato@tsundere.love VSCode and Claude Code is where the best productivity is at. If you aren't using those, you are leaving productivity on the table and letting your team and employer down. Don't do that.
#Productivity #Dev #NodeJS #JavaScript #LLMsAreTheFuture
hey #nodejs fans I need some advice for something new to me
if someone is building code on their mac laptop and we want to deploy it on a different server we need to run nnpm install to grab the right packages for the different cpu architectures
I found docker as one option, a ci pipeline as another. I can think of an approach using shell scripting as well
is there a general consensus around how to handle this?
#devops
A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
#NodeJS #TONBlockchain #EtherHiding #Malware #CyberSecurity
Dynamic fs access has become my favorite Node.js feature. Instead of manually importing files, I just import an entire dataset from a directory. Saves time, scales easily, no typos from manual imports.:)
#NodeJS #JavaScript #programming